PRODUCT FIT / TEST CURRENT RELEASE
Folder Protect for Podcast Source Sessions
Evaluate Folder Protect for one bounded job: reducing unauthorized changes to a supported local folder containing approved audio session masters on a tested Windows PC.
01 / FIT
Use one bounded Windows restriction layer
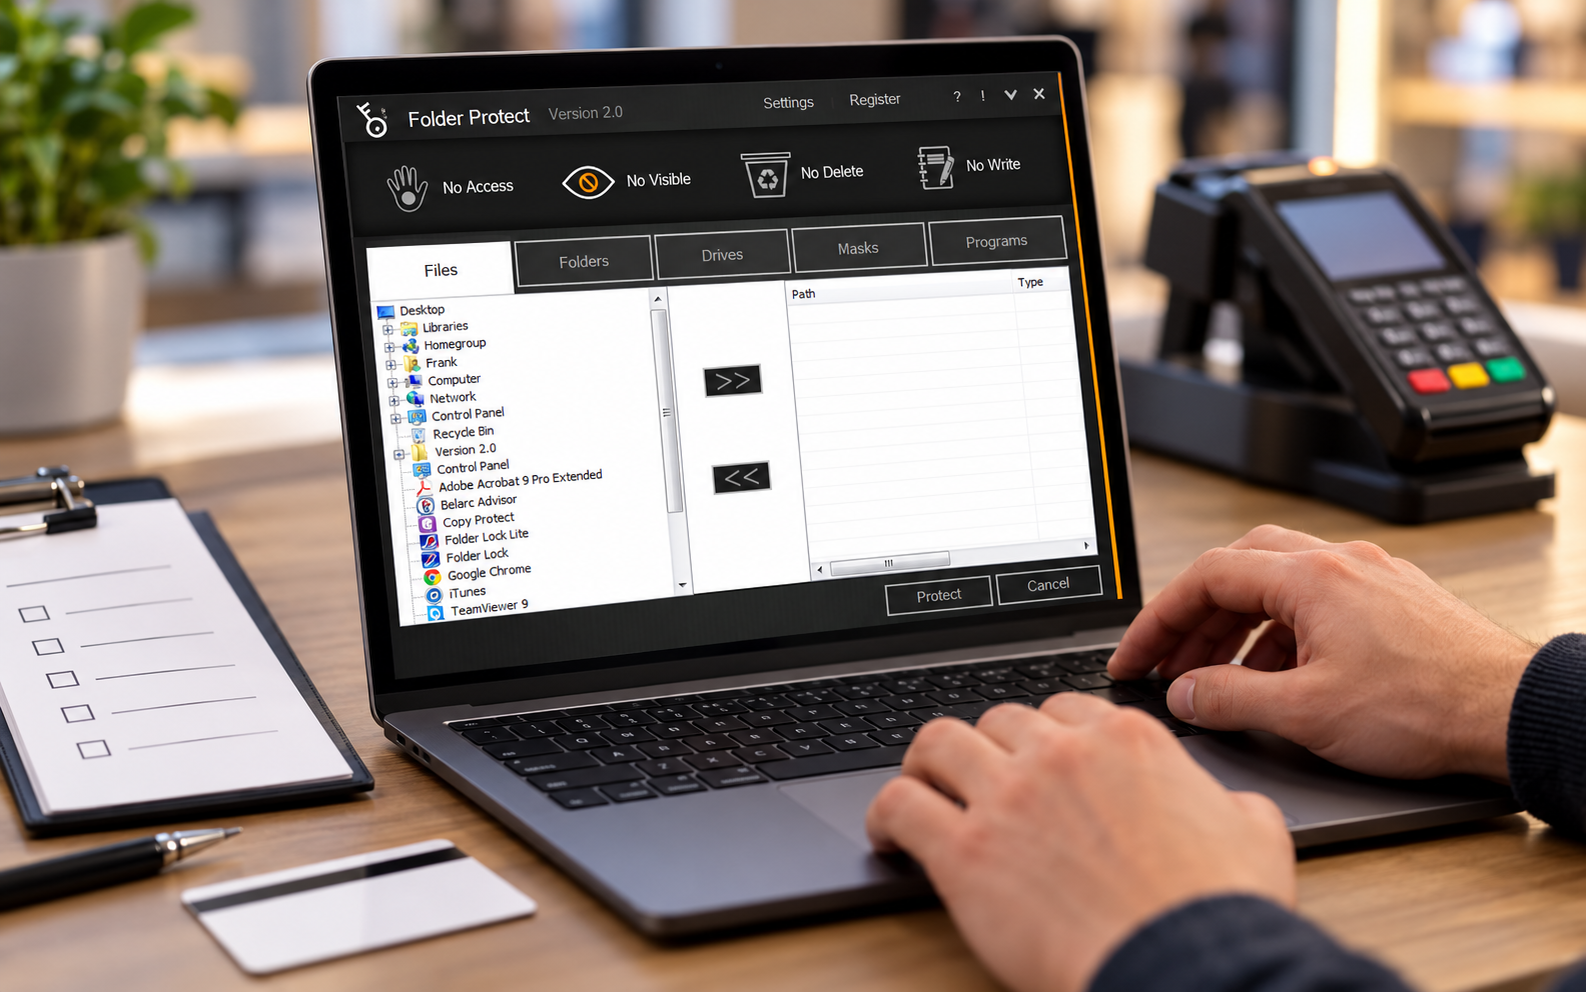
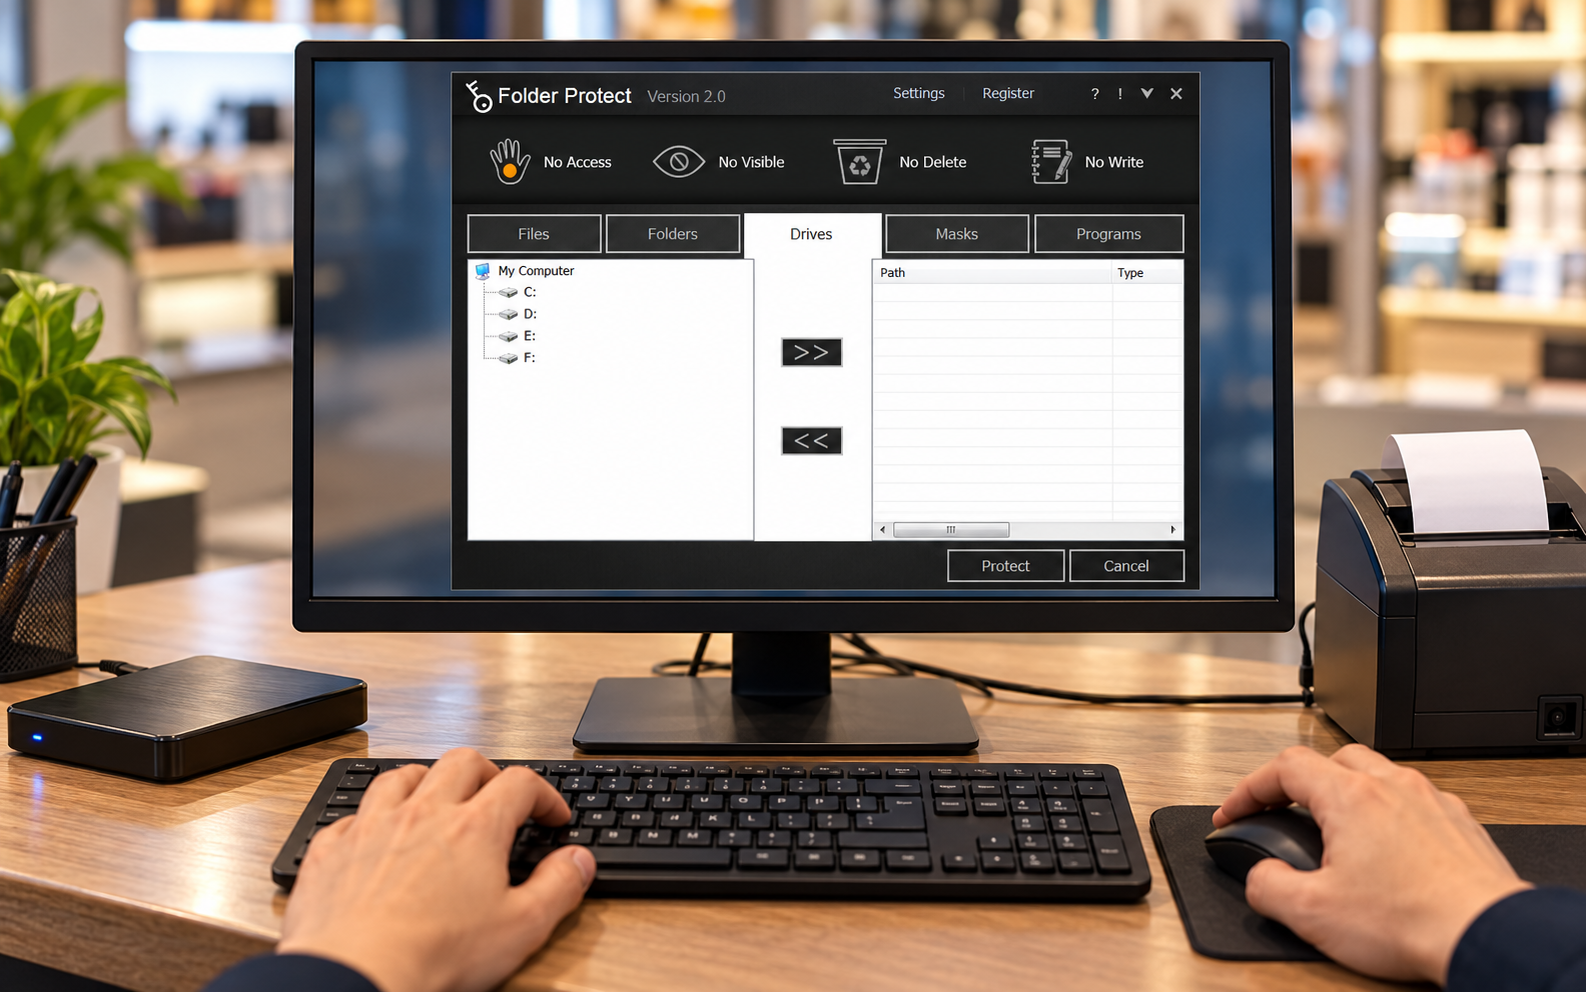
Folder Protect may help restrict access, writing, deletion or visibility for a supported local folder. Video accessibility teams should consider it only after defining the released master, working-copy route, accountable owner, permitted accounts and separate recovery plan. Use only fictional media and non-identifying speaker labels without unreleased media, personal data or credentials during evaluation.
The product does not approve source audio accuracy, establish accessibility or localization quality, authorize delivery, compare versions, manage identities, create immutable change evidence or replace backup.
02 / PILOT
Test the complete lifecycle
- 01
Confirm the current official release, supported Windows edition and documented protection modes.
- 02
Create a fictional folder with fabricated audio session master files and a separately backed-up master.
- 03
Test view, write, delete, restart, sign-out, update and authorized recovery behavior.
- 04
Verify approved editors can create working copies without changing the released master.
- 05
Record password ownership, removal, recovery and retest responsibilities.
03 / INTERFACE
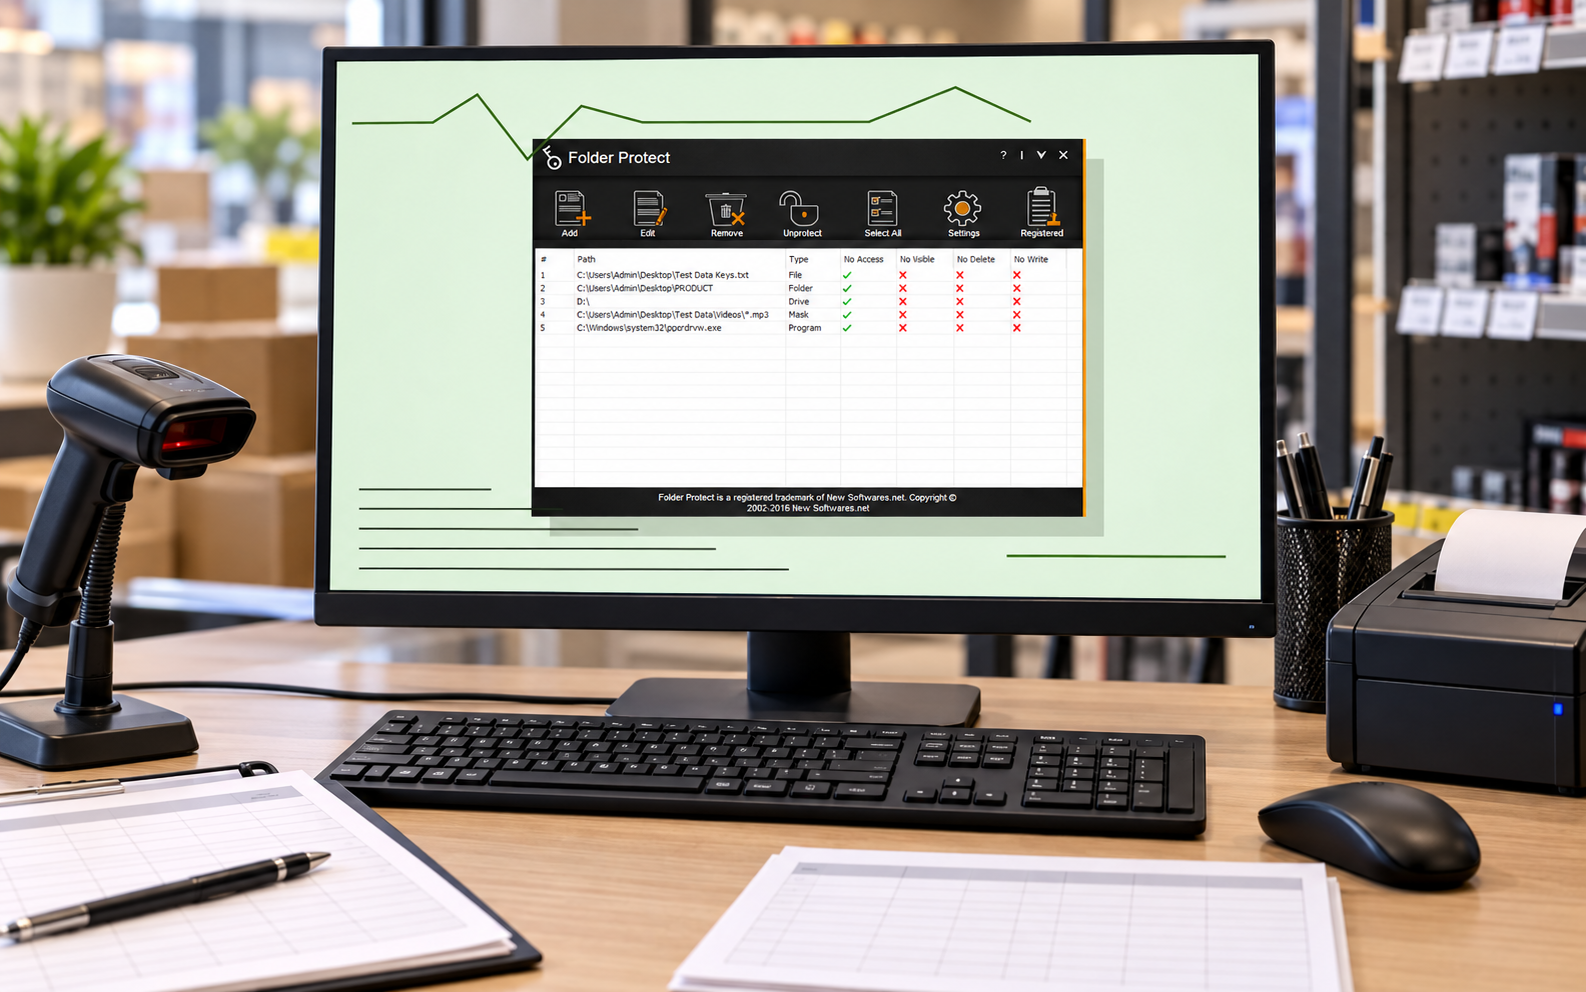
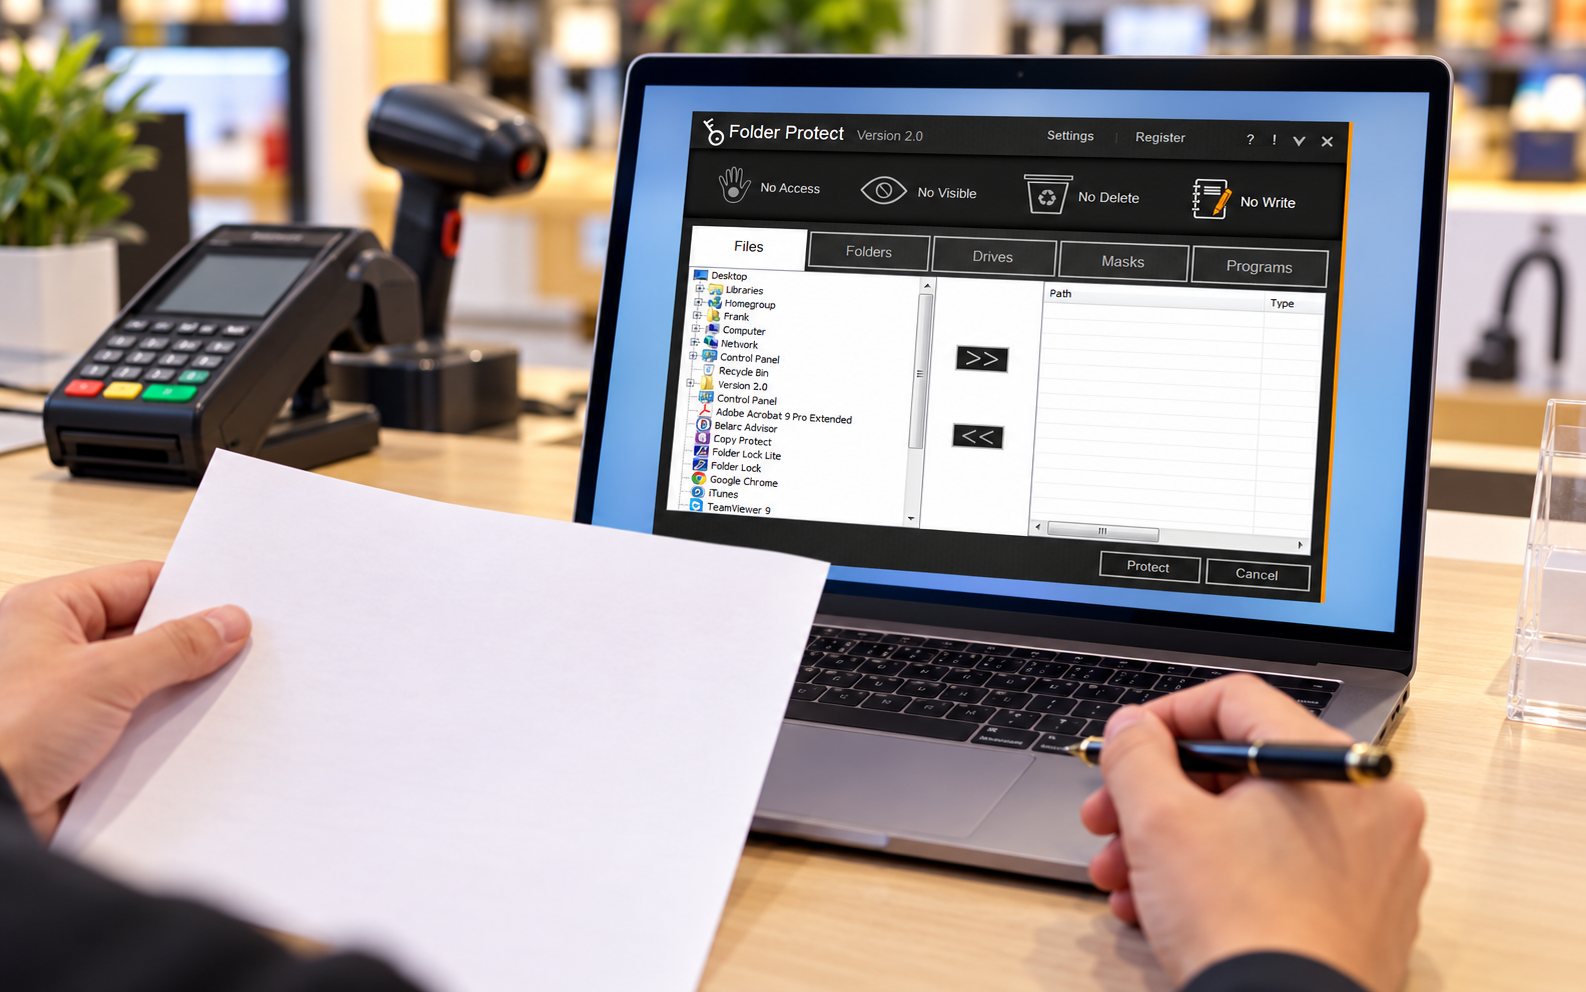
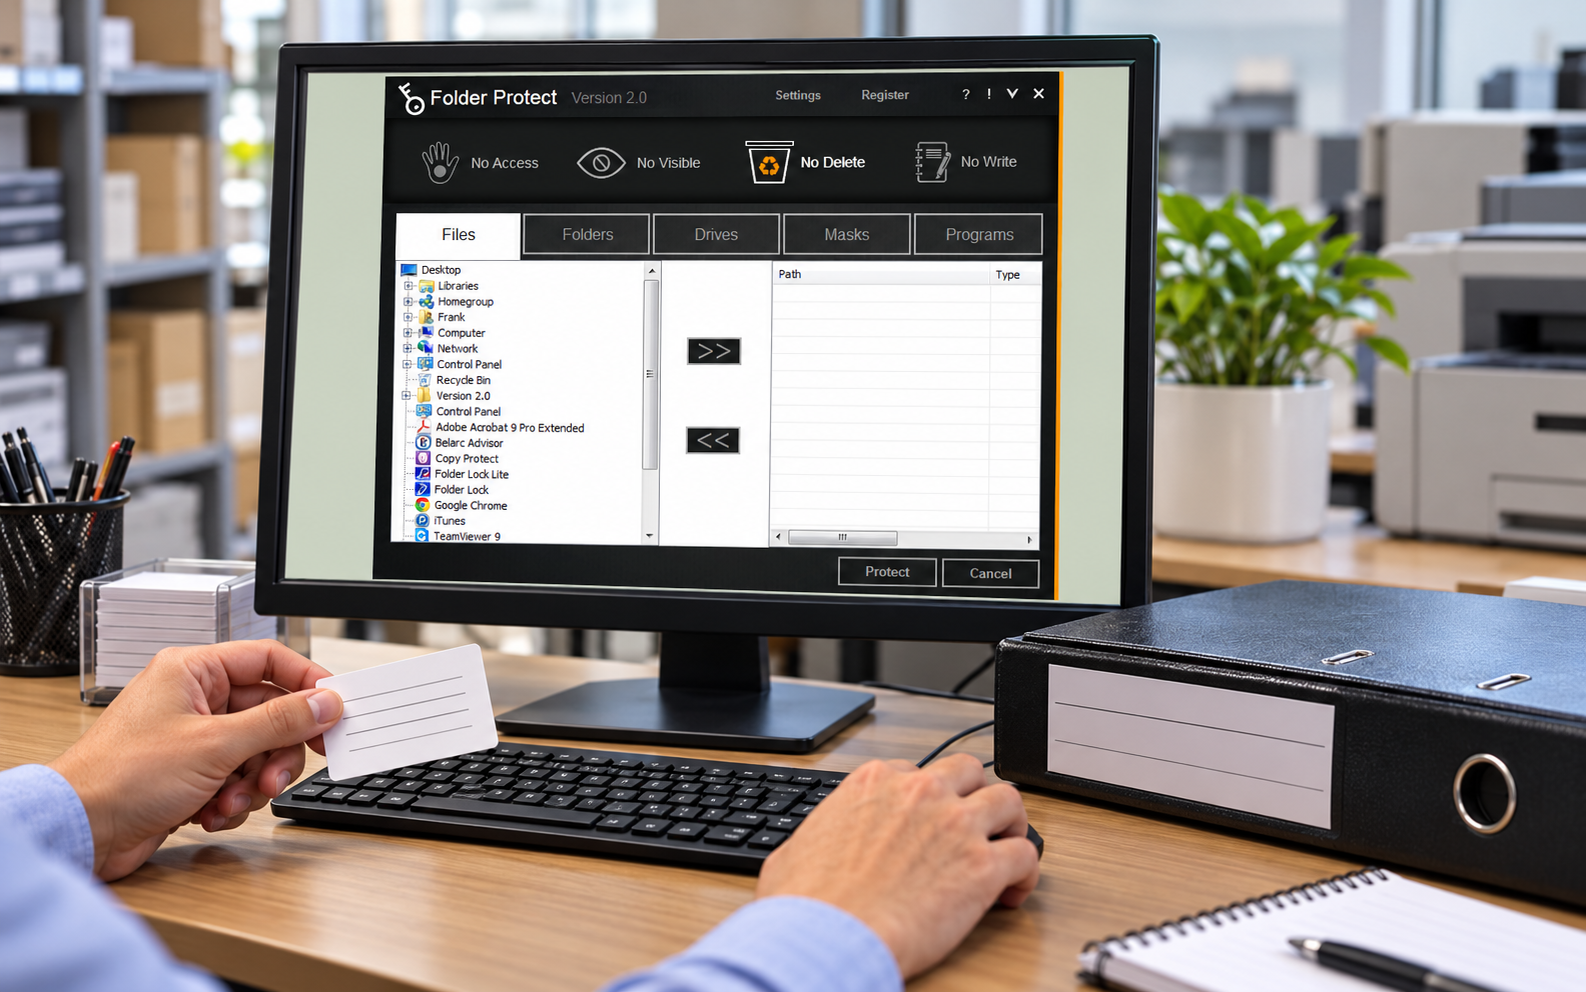
Inspect each relevant control
04 / LIMITS
Keep source audio approval outside the claim
Folder Protect operates at the local Windows file layer. It cannot determine whether source audio timing, synchronization, speaker labels, readability, accessibility conformance, localization or delivery is correct or approved. It does not administer source audio-application or delivery-platform users, recover a source audio-platform account, provide source audio version history, create immutable evidence or guarantee that copies do not exist in email, downloads, chat, temporary storage or another device.
Test the current product and exact intended path. Observe protection during restart, update, password failure and uninstall. Preserve a separate verified backup before testing and never place unreleased media, confidential production notes, personal data or credentials in screenshots. If the template repository is synchronized, evaluate provider permissions and recovery separately. Device encryption, named Windows accounts, endpoint management, repository access, local folder restrictions and backup are distinct controls.
After adoption, record the computer, Windows account, protected path, software version, protection mode, test date, password owner, recovery evidence and next review. Repeat the pilot after software, source audio application, accessibility-review workflow, storage, permission or source audio-editor role changes. A successful block is evidence only for the tested action and path; it is not proof of source audio approval, accessibility conformance or delivery authorization, encryption, secure deletion, regulated retention or business continuity.
A defensible control record identifies the source audio owner, video title, language, audio session format, frame rate, authoritative path, permitted accounts, restriction mode, version ID, accessibility-review date, checksum evidence, recovery owner and next review date. It should not contain unreleased media, personal data, credentials or confidential production notes. Use fictional media and non-identifying speaker labels during every technical test.
Recheck the arrangement after changes to Windows, source audio software, accessibility tooling, localization workflow, storage, Folder Protect, permissions, service accounts or production roles. Confirm both usability and recovery: an authorized editor should read the final audio session master, an unauthorized account should not alter it, and the recovery owner should restore a separately held copy without depending on the protected folder. Preserve unexpected behavior before changing controls.
Keep the claim narrow. Local restrictions may reduce accidental writing, deletion or access on a tested Windows path, but they do not encrypt data, establish source audio accuracy, timing, synchronization, speaker identification, readability, accessibility conformance, localization quality or delivery acceptance, administer identities, provide version history or replace backup. Escalate those requirements to the platform and accountable accessibility owner designed to meet them.
Ask a second editor to follow the written procedure without verbal help. Record whether that person can identify the final master, create a working copy, recognize the version stamp, interpret denied access and find the recovery owner. This usability check reveals ambiguous paths, hidden service-account dependencies and undocumented knowledge before a source audio application, delivery platform, storage or staff change. Correct the procedure, repeat the test with fictional media and retain only minimal evidence.
05 / SOURCES